 Jovis AI
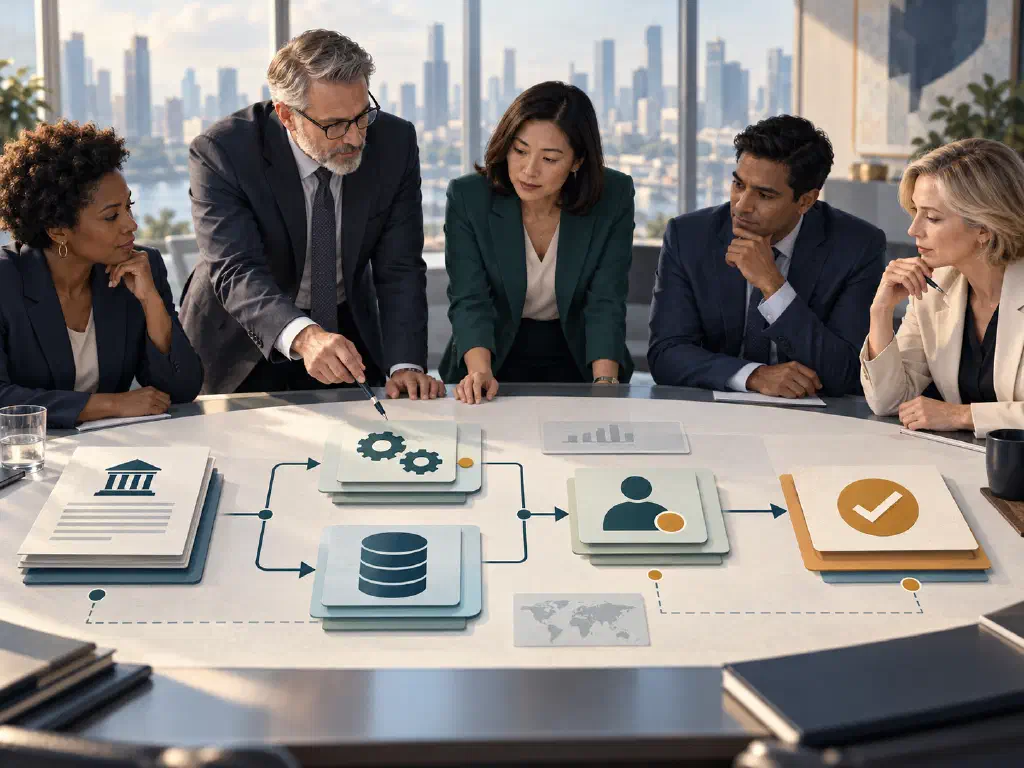
Regulatory change management is the operating discipline of turning a new or amended requirement into a decision: does it apply, what business activity does it affect, what must change, who owns the response, and how will leaders know it is complete?
For an executive team, the failure is rarely that nobody heard about a rule. It is that a legal update, control inventory, product process, vendor dependency, and delivery plan never meet in one reviewable path. The organization either creates an alert queue nobody can resolve or treats a legal summary as though it were an implementation plan.
AI can assist the preparation work: extracting obligations from approved sources, finding potentially affected policies and systems, and assembling the evidence for an impact review. It should not decide applicability, give legal advice, certify compliance, or silently change a control. Those calls belong with the people who own the business, risk, legal, security, and product consequences.
Start with the decision, not the regulatory feed
“Monitor regulations” is an activity, not a useful operating job. The first version should answer one bounded decision, such as:
For material changes affecting our use of customer data in a named market, decide whether the change applies, which business services require assessment, and whether an executive sponsor must approve a remediation plan.
That sentence establishes the jurisdiction, subject, threshold, output, and decision owner. It also prevents a common failure mode: a broad feed of documents routed to a compliance team with no connection to the operating model.
The NIST AI Risk Management Framework is useful here as a management lens, not as a compliance shortcut. Its core functions are govern, map, measure, and manage. A change workflow needs all four: governance establishes authority; mapping links a change to the business; measurement tests exposure and readiness; management chooses and tracks a response.
If the change concerns AI, distinguish a rule that governs the organization’s AI use from a rule that governs a particular model, supplier, geography, or customer interaction. For example, the European Commission states that the EU AI Act entered into force on 1 August 2024 and became generally applicable on 2 August 2026, with exceptions and staggered obligations. That makes applicability and timing questions essential, rather than something a generic “AI compliance” label can settle. See the Commission’s AI Act regulatory-framework overview.
Build a change record before asking AI to summarize anything
A summary is easy to circulate and difficult to operate. A change record forces the team to preserve what it knows, what it assumes, and what it still needs to determine.
| Field | What it should establish |
|---|---|
| Source and version | The authoritative document, issuing body, publication date, effective date, and retrieval date |
| Requirement statement | The relevant obligation or proposed change, with a citation to its source section |
| Scope hypothesis | Jurisdictions, legal entities, products, customers, data, or activities that may be in scope |
| Impacted business services | The processes and systems that could be affected, plus a named service owner |
| Decision and deadline | The next decision, who is accountable, and the date by which it must be made |
| Evidence and open questions | Supporting records, interpretation questions, dependency gaps, and confidence limits |
| Response status | Not applicable, assess, plan, implement, validate, or closed, with a rationale |
An AI-assisted workflow can draft the requirement statement and propose links to an internal policy library, process catalogue, contract inventory, or system register. Treat every proposed link as a lead. A matching phrase does not establish legal relevance, and an old policy document may not represent how work is actually performed.
This is the same discipline behind trusted AI answers: a useful answer needs approved sources, defined terms, access boundaries, and a way to inspect the evidence. In regulatory work, the cost of confusing a plausible narrative with an established fact can be especially high.
Run four distinct stages
Keeping detection, interpretation, impact, and response separate makes the workflow faster to challenge and safer to operate.
1. Detect and qualify the change
Use a curated list of primary regulators, official gazettes, and subscribed legal sources. Record whether the item is a proposal, final rule, guidance, enforcement action, or interpretation. Do not let an AI system turn a consultation, a press report, or a vendor blog into an obligation.
The first human review should make a simple call: ignore, watch, or assess. “Watch” is a valid decision when the effective date, implementing rules, or applicability facts are not yet known. It should include a named owner and a review trigger, not a vague promise to revisit it.
2. Interpret with the appropriate authority
Legal, compliance, privacy, or a sector specialist should establish the interpretation path appropriate to the organization. AI can surface defined terms, cross-references, and differences between versions; it cannot replace advice from qualified counsel or an accountable control owner.
The output should distinguish three statements:
- Text: what the authoritative source says and where.
- Interpretation: how the organization currently understands its application.
- Question: what requires external advice, regulator engagement, or further fact finding.
That separation is more useful than a single “compliant/not compliant” label. It gives executives visibility into uncertainty before it becomes a late delivery surprise.
3. Map the impact to real work
The working question is not “which teams should know?” It is “which business service could fail to meet the requirement, and who can show how it works today?”
For each affected service, map the journey from input to outcome: customer or employee touchpoint, data category, decision or action, supporting system, supplier involvement, control, record retained, and accountable owner. A change to a disclosure requirement, for example, may involve product copy, customer-support scripts, consent records, a marketing workflow, and a vendor-provided interface. Each is a different implementation question.
This is where executives can remove the most friction. Ask teams to reuse their operational evidence rather than create a second reporting universe. An evidence map built for a service owner can also support risk, audit, security, and product review when its definitions and access rules are clear. Business-data context explains why a system name or a number alone is not enough to support a decision.
4. Decide, deliver, and validate
The response plan should carry the decision, not merely a project status. For each material change, document:
- the applicable requirement and interpretation basis;
- the service or control gap being addressed;
- the chosen response, alternatives considered, and residual risk accepted;
- the accountable executive and delivery owner;
- the evidence that will demonstrate implementation; and
- the validation date, escalation trigger, and closure authority.
Separate approval of the plan from evidence of completion. A green milestone is not proof that a control operates as intended. The same distinction matters in an AI internal-audit workflow: assembling evidence can be assisted, while independent judgment about sufficiency remains accountable work.
Use AI for connection work, not legal authority
The most promising contribution of AI is reducing the time spent reconstructing context across approved systems. A bounded agent may prepare a review packet that connects the new text to relevant policies, process descriptions, tickets, control tests, implementation plans, and past decisions. It can also identify missing evidence and produce a concise change brief for the executive sponsor.
The boundary matters. The agent should not:
- declare a requirement applicable or inapplicable without accountable review;
- advise on legal interpretation or represent a conclusion as counsel’s advice;
- access every document just because a topic appears relevant;
- alter policy, product behavior, customer communications, or vendor terms;
- close a remediation item on the basis of its own summary.
Apply the least access needed for the review job, and keep the person, tool, and underlying resource in the authorization path. The practical design principles in AI-agent permissions and access control are directly relevant: read, propose, and execute are different authorities, and access should be enforced outside the model.
Give the executive team a decision-ready view
Executives do not need a weekly recital of regulatory headlines. They need a compact view of material exposure and stalled decisions. A useful cadence separates the portfolio into four lanes:
| Lane | Executive question | Required evidence |
|---|---|---|
| Emerging | What could become material, and when will we know more? | Source, jurisdiction, owner, next trigger |
| Assessing | What part of the business may be affected? | Scope hypothesis, services, open interpretation questions |
| Responding | What decision or resource is needed now? | Options, delivery plan, dependencies, residual risk |
| Validating | What proves the response works? | Test or control evidence, exception status, closure owner |
Keep this review connected to an existing risk, product, or operating cadence. A new steering committee is rarely the first answer. If the decision affects a top business risk, bring it into the enterprise-risk conversation; if it affects a specific release or market launch, put it where that decision already happens.
For leaders building AI-enabled workflows, the longer-term opportunity is shared, governed memory: the organization should not have to rediscover the same requirement, rationale, service context, and owner every quarter. That is an operating-model goal, not a claim that a tool can make regulatory responsibility disappear.
A practical first pilot
Choose one regulated product area, one geography, and one change type. Run the workflow retrospectively on a change your organization has already handled. Compare the new record with what happened in practice:
- Did the source record preserve the exact version and effective date?
- Could the team identify the affected service and accountable owner without a broad email search?
- Were legal interpretation, operating facts, and unresolved questions kept distinct?
- Did the planned evidence actually support the closure decision?
- Where did the workflow produce noise, omit context, or expose an access problem?
Use the findings to refine the source boundary, business-service map, and escalation thresholds before monitoring new changes. This resembles a controlled 30-day AI-agent pilot: start in shadow mode, test against known outcomes, and make a go-or-stop decision based on the complete workflow rather than the fluency of a draft.
Jovis gives teams a governed workspace for investigating business questions across approved sources. A reasonable place to explore that approach is a single regulatory-change review where legal, compliance, and business owners need a shared evidence packet before an accountable decision.